About LTK Soft
We built our reputation — in the hardest environments first.
LTK Soft was founded in 2008 to solve one of software's most demanding problems: building law enforcement software where downtime, security gaps, and audit failures were not acceptable. Eighteen years later, that discipline defines everything we build — in insurance, healthcare, technology, and beyond.
US-based leadership. Global delivery. Founded 2008 · 300+ projects · Clients in 32 countries · 4 ISO certifications
We've spent 18 years building systems where failure isn't an option. That standard applies to every client, every project, every deployment.
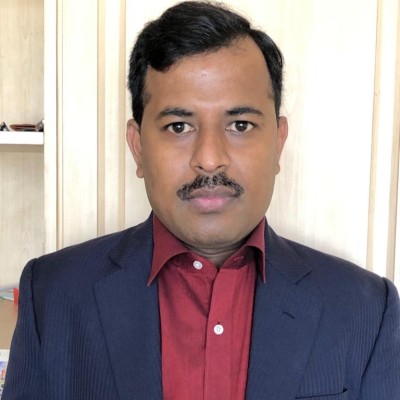 Kesavulu ReddyCEO, LTK Soft
01Our story
Why we started in law enforcement
LTK Soft was founded in 2008 with a deliberate choice: start in the most demanding compliance environment in software. Law enforcement systems handle FBI CJIS data — criminal justice information that, if breached, compromises investigations, endangers officers, and triggers federal consequences. There is no "ship fast and fix later" in that world. Either the system meets the requirements from architecture to deployment, or it isn't built.
That founding discipline shaped every practice we developed. Compliance-first architecture. Security controls designed in, not added after. Audit documentation prepared before development begins. Systems engineered for the worst day an agency will ever experience. Over the years we applied the same discipline to insurance, healthcare, fintech, telecom, and SaaS products — and today to AI agents and knowledge bases that keep data inside our clients' own cloud.
Today we work across Insurance & Financial Services, Healthcare, Technology & SaaS, and Public Safety & Government — and with any business whose data is too important to hand to a public AI tool. 300+ projects, clients in 32 countries, and nearly two decades delivering secure, production-grade software.
02What we believe
Three things we believe that most technology firms don't
01
Compliance is architecture, not certification
A compliance certification tells you a vendor passed a checklist. We build compliance into the system architecture from the first design decision. CJIS, HIPAA, SOC 2 — these aren't badges. They're design constraints: access controls, audit trails, encryption, and documentation planned before the first line of code.
02
We'll tell you when we're not the right fit
We've declined projects we couldn't deliver at our standard. We've told clients their approach wouldn't work before they spent money building it. We've suggested simpler solutions when the situation called for it. This costs us revenue. It earns us long relationships — one of our engineering partnerships lasted 16 years.
03
Operational certainty is the product — not the software
Software is the mechanism. What our clients are buying is the certainty that a critical system will work on the worst day they face, pass the audit they didn't anticipate, and be maintainable by their team five years after we've delivered it. That's what we engineer for. If the system works only on good days, it wasn't engineered correctly. It's been our operating standard since 2008.
03Fit
Who we work best with
We're the right fit if
- Your data is sensitive — customer, patient, financial, or criminal justice information
- You've had an AI project that never made it out of proof-of-concept into production
- A security breach would be career-defining for someone in your organization
- You've had a vendor fail a compliance audit before and can't afford to repeat it
- You need senior oversight, not a rotating junior bench
- You want to own your code, your IP, and your infrastructure — no lock-in
We're probably not the right fit if
- You need the cheapest possible option
- Your timeline is 'we needed this yesterday' with no room for proper scoping
- You want us to build first and think about compliance later
- You're looking for a vendor who will just say yes to every requirement
- You want a large team of juniors billed by the hour
If you're not sure which column fits your situation — that's exactly what our 30-minute discovery call is for.
04Leadership
The people accountable for your project
Kesavulu Reddy
CEO
Co-founded LTK Soft in 2008 with a specific mission: build law enforcement software to FBI CJIS Security Policy requirements from day one. Over 20 years of enterprise software architecture experience. Led engineering for 16 years on law enforcement software used by police and sheriff's offices across the US — environments where a security failure has federal consequences. Expanded that discipline into insurance automation, healthcare, cloud architecture, and AI. Leads technical architecture and strategic delivery.
View LinkedIn profile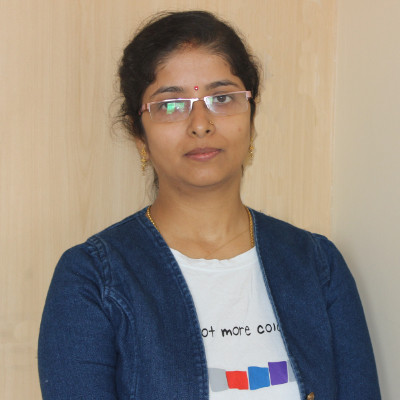
Khushi Reddy
CIO
Drives information strategy, compliance operations, and technology governance at LTK Soft. Maintains LTK Soft's internal compliance governance framework — the ISO management systems, HIPAA, CJIS, and SOC 2 control documentation, audit preparation protocols, and security policies behind every engagement. The operational discipline that makes our delivery model work starts here.
View LinkedIn profile05Our path
How 18 years of high-stakes software compounded into an advantage
- 2008
Founded on the hardest problem first
LTK Soft launched with law enforcement software — the start of a 16-year engineering partnership with a US law enforcement technology provider, building software used by police and sheriff's offices to CJIS Security Policy requirements.
- 2010s
A global client base
Insurance, fintech, healthcare, telecom, and SaaS clients across 32 countries — including claims automation for Argo Global and subcontract work for Fortune 500 and global brands in automotive, consumer goods, retail, and pharmaceuticals.
- 2020s
AI in production
AI features shipped into long-running client platforms, followed by AI agents and RAG knowledge bases that run inside each client's own cloud — so sensitive data never leaves their control.
- Today
18 years. 300+ projects. Clients in 32 countries.
Insurance & Financial Services, Healthcare, Technology & SaaS, Public Safety & Government, and more. US-based leadership and the same senior team — applying the discipline we learned in law enforcement to AI, cloud, and custom software.
06Certifications
Certifications and security standards
Certified
ISO 27001:2022
Certificate No. IS20170815833
Certified by UK Management Certification Limited
Certified
ISO/IEC 20000-1:2018
Certificate No. IS20170815832
Certified by UK Management Certification Limited
Designed to
CJIS Security Policy
Law enforcement software since 2008
Designed to
HIPAA Requirements
Healthcare systems built to HIPAA requirements
Designed to
SOC 2 Aligned
Security controls best practices
Designed to
AWS Partner Network
Registered AWS partner
Our ISO certifications are issued by an independent certification body. CJIS and HIPAA are not certifications any vendor can hold — they are requirements we design and document against, so your own audits go smoothly.
For our full delivery methodology → See how we work
Evaluating a long-term technology partner? Start here.
We'll have an honest conversation about your project, your compliance requirements, and whether we're the right fit. If we're not, we'll tell you — and suggest who is.